
Abuse Shield: centralised server protection against IP abuse
Abuse Shield: centralised server protection against IP abuse
Why protecting each server separately no longer scalesMost small and mid-sized organisations in Catalonia run more than one server. A web front end in...
Why protecting each server separately no longer scales
Most small and mid-sized organisations in Catalonia run more than one server. A web front end in Barcelona, a database node in Lleida, a mail relay in Girona, perhaps a staging box in Tarragona. Each one has its own firewall rules, its own logs and, if you are lucky, its own fail2ban installation. The problem is not that fail2ban is bad — it is a solid, well-understood tool. The problem is that it is local by design. A server only knows what it has seen itself.
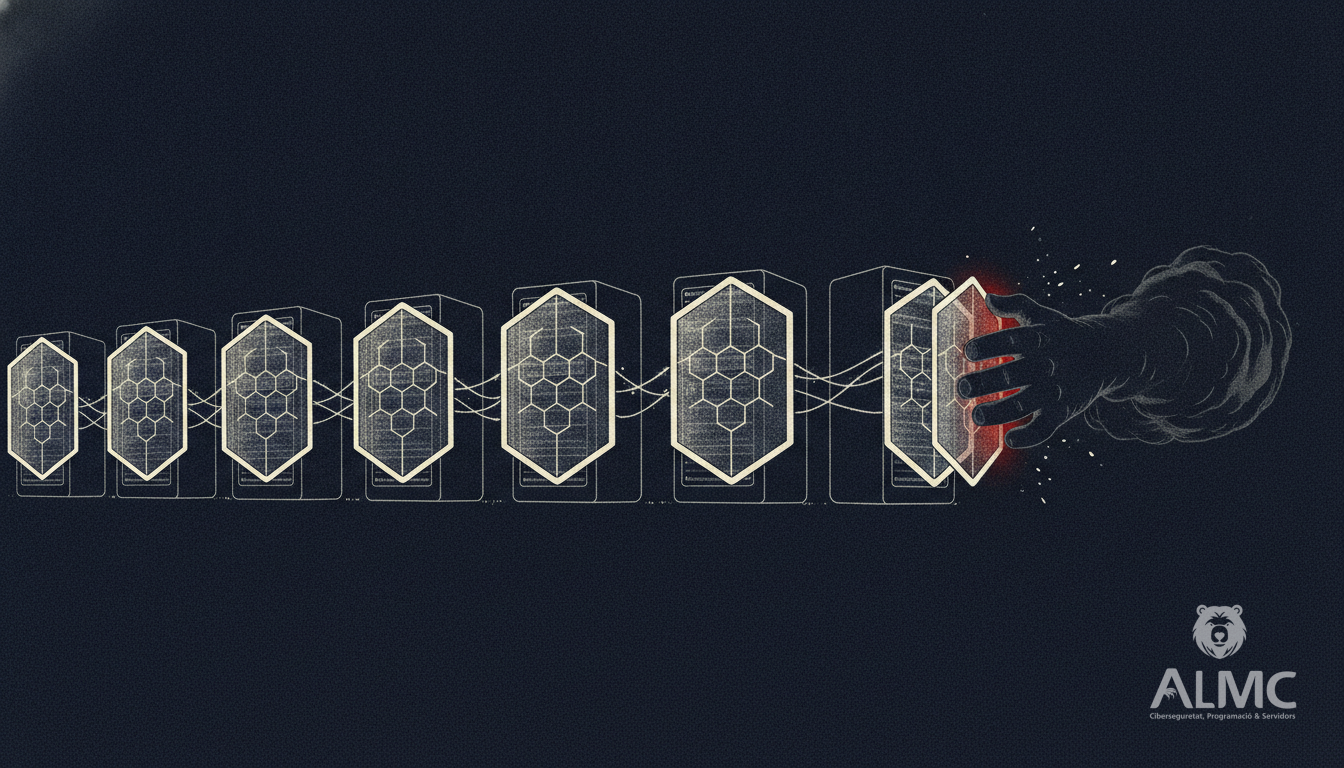
That creates a blind spot that attackers exploit constantly. A botnet probes your Barcelona node on Monday, gets banned after a few hundred attempts, and simply moves to the Tarragona machine on Tuesday, where nobody has ever seen that address. Each server learns the same lesson from scratch, at your expense in CPU, bandwidth and log noise. Recent high-profile PHP runtime vulnerabilities have reminded us how quickly a single unpatched service can turn into remote code execution, so reducing the number of malicious requests that actually reach your application is no longer a nice-to-have.
What Abuse Shield actually does
Abuse Shield is the service we built at ALMC.es to close that gap. Instead of configuring fail2ban by hand on every machine, you connect your servers to a single control plane that handles three things:
- Automatic blocking of malicious IPs. Detection rules run centrally and bans are applied consistently, so a repeat offender is stopped wherever it appears.
- Managed fail2ban across multiple machines. Jails, filters and ban durations are deployed and updated from one place, which means no more drift between servers and no more forgotten configurations after a migration.
- A shared IP reputation feed. When one of your servers detects an abusive address, every other server in your fleet learns about it immediately. The knowledge compounds instead of resetting.
The effect is cumulative. The more machines you connect, the more intelligence each one has, and the less noise reaches your applications, your logs and your support team.
Who benefits most
Three profiles tend to see value fastest. System administrators get their evenings back: no more SSH sessions to compare jail configurations or chase a ban that never propagated. Hosting companies can offer a consistent security baseline across dozens of customer machines without hiring proportionally more staff. And SMEs with their own servers — the kind of company that has a rack in a local data centre and one person who "knows the servers" — gain protection that does not depend on that person being on holiday.
How it fits with GDPR and day-to-day operations
Centralising security data raises a legitimate question: what are you collecting, and where? Abuse Shield works with IP addresses and connection metadata, which are personal data under the GDPR. Our approach keeps processing within the EU, limits retention to what is needed for detection, and documents the legal basis for processing. For most clients this is a straightforward legitimate-interest assessment, but we help you put it in writing so your DPA and your records of processing stay coherent.
Operationally, the service is designed to be non-disruptive. Bans are reversible, whitelists protect your own monitoring and office ranges, and every action is logged so you can explain why an address was blocked. If you already run fail2ban, migration is incremental: connect one server, observe, then roll out the rest.
Where to start
You do not need to connect your entire fleet on day one. Start with the server that receives the most unwanted traffic — usually the public web front end — and let the shared reputation feed do the rest. Within a few weeks you will have a clearer picture of who is probing your infrastructure and, more importantly, a single place to act on it.
If your servers are spread across providers or offices in Lleida, Barcelona or anywhere else in Catalonia, that is exactly the scenario Abuse Shield was designed for. Centralised protection, managed fail2ban and shared IP reputation: one control plane instead of a dozen separate fights.
Related
- How to Harden Your Servers with Fail2ban and IP Reputation Feeds
- Fail2ban: Your First Line of Defense Against Unauthorized Server Access
- Critical libssh2 flaw: urgent patch for SSH servers
- Desarrollo web
Put these ideas into practice
Talk to ALMC about a solution for your business. Explore your options or contact our team.