
Abuse Shield: Centralised Server Protection for Catalan SMEs
Abuse Shield: Centralised Server Protection for Catalan SMEs
Why scattered defences leave you exposedMost SMEs and hosting providers in Catalonia run more than one server: a web front end, a database, a mail rel...
Why scattered defences leave you exposed
Most SMEs and hosting providers in Catalonia run more than one server: a web front end, a database, a mail relay, maybe a staging box in a different rack. Each one usually has its own firewall rules and its own fail2ban installation, configured at different times by different people. The result is predictable. An attacker hammers one machine, gets blocked there, moves to the next and starts again from zero. Your defences never learn from each other, and your team spends hours copying rules between machines instead of improving the service.
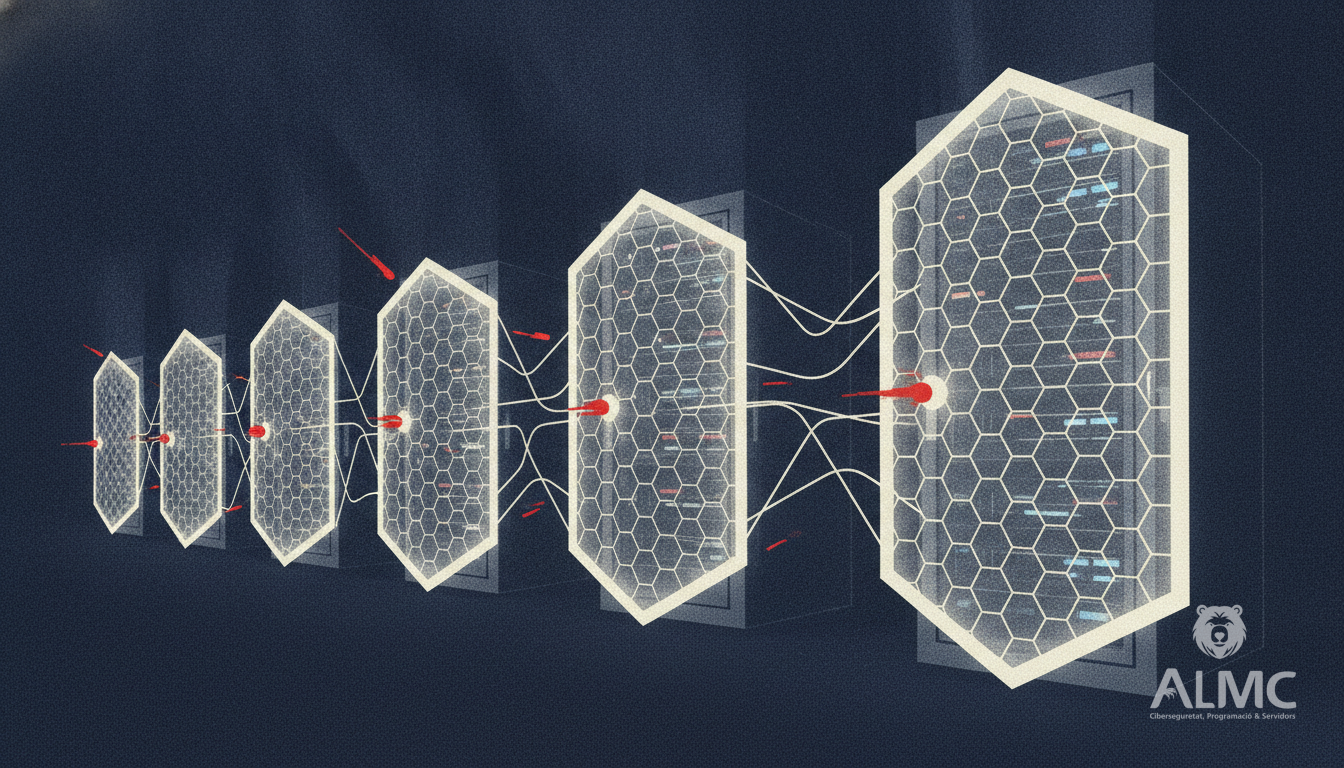
This is the gap that Abuse Shield closes. Instead of treating each server as an isolated island, it centralises server security so that a threat detected anywhere is blocked everywhere.
What centralised protection actually means
Abuse Shield combines three capabilities that work best together:
- Automatic blocking of malicious IPs. Repeated failed logins, abusive request patterns and known bad actors are blocked without waiting for a human to notice.
- Managed fail2ban across multiple machines. The same jail logic and thresholds are applied consistently, so you no longer inherit a decade of ad-hoc configuration drift.
- A shared IP reputation feed. When one server identifies an abusive address, every server in your fleet benefits from that knowledge immediately.
The practical effect is that your infrastructure behaves like a single defended perimeter rather than a collection of loosely connected boxes. For a hosting company managing dozens of customer VPS instances, or a Lleida-based SME with three on-premise servers and a cloud node, that difference is significant.
The new evasion tricks you should know about
Attackers are not standing still. Recent research has shown that malware authors now try to manipulate the very tools used to analyse their code. One documented technique, sometimes called prompt injection against security scanners, involves placing decoy instructions inside code comments so that an AI-assisted analyser refuses to continue inspecting the file. Other campaigns have stuffed malicious packages with repetitive text designed to exhaust a model's context window, or have hidden payloads behind sections labelled as confidential. The common thread is that automated analysis can be steered, delayed or blinded.
What does this mean for a systems administrator in Girona or Tarragona? It means you should never rely on a single layer of defence, and you should be sceptical of any tool that promises to catch everything automatically. Deterministic controls such as fail2ban, rate limiting and IP reputation remain essential precisely because they do not depend on a model's judgement. Abuse Shield is built around that principle: automated, predictable blocking that does not get talked out of doing its job.
Built for the realities of Spanish and EU compliance
Keeping logs of blocked addresses and authentication failures is not just an operational nicety. Under the GDPR, and in the context of incidents that may need to be reported to the AEPD, having a clear, centralised record of who tried what and when is valuable. Abuse Shield gives you that audit trail across your whole fleet rather than scattered across machines. For companies in regulated sectors, or those serving public administrations, this traceability simplifies both internal reviews and conversations with clients who ask how their data is protected.
Who benefits most
- Systems administrators who want one dashboard and one policy instead of ten divergent configurations.
- Hosting companies that need to protect customer servers without multiplying operational overhead.
- SMEs with their own servers that lack a dedicated security team but still face the same automated attacks as larger firms.
In all three cases the value is the same: less time firefighting, fewer repeated incidents, and a clearer picture of what is hitting your infrastructure.
Getting started without disruption
Rolling out Abuse Shield does not require ripping out your existing setup. The usual approach is to connect your servers, import your current fail2ban rules as a starting point, and let the shared reputation feed begin learning from real traffic. Within days you typically see the same abusive addresses appearing across multiple machines, which is exactly the pattern that isolated defences miss. From there, tuning thresholds and reviewing blocked IPs becomes a routine task rather than an emergency.
Security works best when it is consistent. Centralising it is the simplest way to achieve that consistency without adding headcount.
Related
- How to Harden Your Servers with Fail2ban and IP Reputation Feeds
- Fail2ban: Your First Line of Defense Against Unauthorized Server Access
- Critical libssh2 flaw: urgent patch for SSH servers
- Desarrollo web
Put these ideas into practice
Talk to ALMC about a solution for your business. Explore your options or contact our team.